Linchakin

OFRAK - Unpack, Modify, And Repack Binaries

 December 25, 2022     No comments   

OFRAK (Open Firmware Reverse Analysis Konsole) is a binary analysis and modification platform. OFRAK combines the ability to:

  • Identify and Unpack many binary formats
  • Analyze unpacked binaries with field-tested reverse engineering tools
  • Modify and Repack binaries with powerful patching strategies

OFRAK supports a range of embedded firmware file formats beyond userspace executables, including:

  • Compressed filesystems
  • Compressed & checksummed firmware
  • Bootloaders
  • RTOS/OS kernels

OFRAK equips users with:

  • A Graphical User Interface (GUI) for interactive exploration and visualization of binaries
  • A Python API for readable and reproducible scripts that can be applied to entire classes of binaries, rather than just one specific binary
  • Recursive identification, unpacking, and repacking of many file formats, from ELF executables, to filesystem archives, to compressed and checksummed firmware formats
  • Built-in, extensible integration with powerful analysis backends (angr, Binary Ninja, Ghidra, IDA Pro)
  • Extensibility by design via a common interface to easily write additional OFRAK components and add support for a new file format or binary patching operation

See ofrak.com for more details.

GUI Frontend

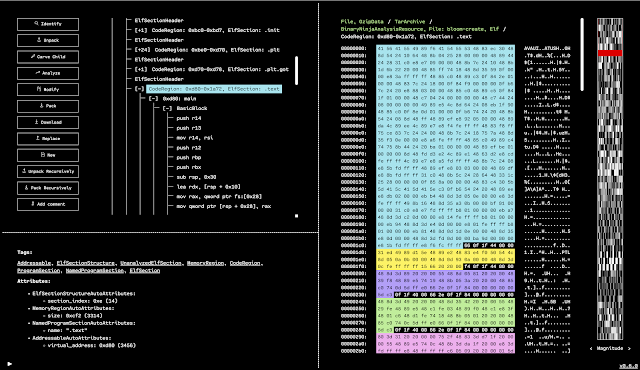
The web-based GUI view provides a navigable resource tree. For the selected resource, it also provides: metadata, hex or text navigation, and a mini map sidebar for quickly navigating by entropy, byteclass, or magnitude. The GUI also allows for actions normally available through the Python API like commenting, unpacking, analyzing, modifying and packing resources.
Getting Started

OFRAK uses Git LFS. This means that you must have Git LFS installed before you clone the repository! Install Git LFS by following the instructions here. If you accidentally cloned the repository before installing Git LFS, cd into the repository and run git lfs pull.

See docs/environment-setup for detailed instructions on how to install OFRAK.

Documentation

OFRAK has general documentation and API documentation. Both can be viewed at ofrak.com/docs.

If you wish to make changes to the documentation or serve it yourself, follow the directions in docs/README.md.

License

The code in this repository comes with an OFRAK Community License, which is intended for educational uses, personal development, or just having fun.

Users interested in OFRAK for commercial purposes can request the Pro License, which for a limited period is available for a free 6-month trial. See OFRAK Licensing for more information.

Contributing

Red Balloon Security is excited for security researchers and developers to contribute to this repository.

For details, please see our contributor guide and the Python development guide.

Support

Please contact [email protected], or write to us on the OFRAK Slack with any questions or issues regarding OFRAK. We look forward to getting your feedback! Sign up for the OFRAK Mailing List to receive monthly updates about OFRAK code improvements and new features.


This material is based in part upon work supported by the DARPA under Contract No. N66001-20-C-4032. Any opinions, findings and conclusions or recommendations expressed in this material are those of the author(s) and do not necessarily reflect the views of the DARPA. Distribution Statement “A” (Approved for Public Release, Distribution Unlimited).

Adblock test (Why?)


You may be interested in:
>> Is a Chromebook worth replacing a Windows laptop?
>> Find out in detail the outstanding features of Google Pixel 4a
>> Top 7 best earbuds you should not miss

Related Posts:
>> Recognizing 12 Basic Body Shapes To Choose Better Clothes
>>Ranking the 10 most used smart technology devices
>> Top 5+ Best E-readers: Compact & Convenient Pen
Read More
  • Share This:  
  •  Facebook
  •  Twitter
  •  Google+
  •  Stumble
  •  Digg

OWASSRF – New Exploit Let Attacker Execute Remote Code on Microsoft Exchange Server

 December 22, 2022     No comments   

OWASSRF

There is a new exploit chain dubbed, OWASSRF that threat actors are actively exploiting to gain arbitrary code execution through Outlook Web Access (OWA) on vulnerable servers that bypasses ProxyNotShell URL rewrite mitigations.

A recent investigation by CrowdStrike Services found that Microsoft Exchange ProxyNotShell vulnerabilities are probably enabled the common entry vector for several Play ransomware intrusions:-

The relevant logs were reviewed by CrowdStrike and no evidence of initial access exploiting CVE-2022-41040 was found. 

ProxyNotShell and Exchange Architecture Primer

There are two major components that make up a Microsoft Exchange server:- 

  • The frontend
  • The backend
Exchange Architecture

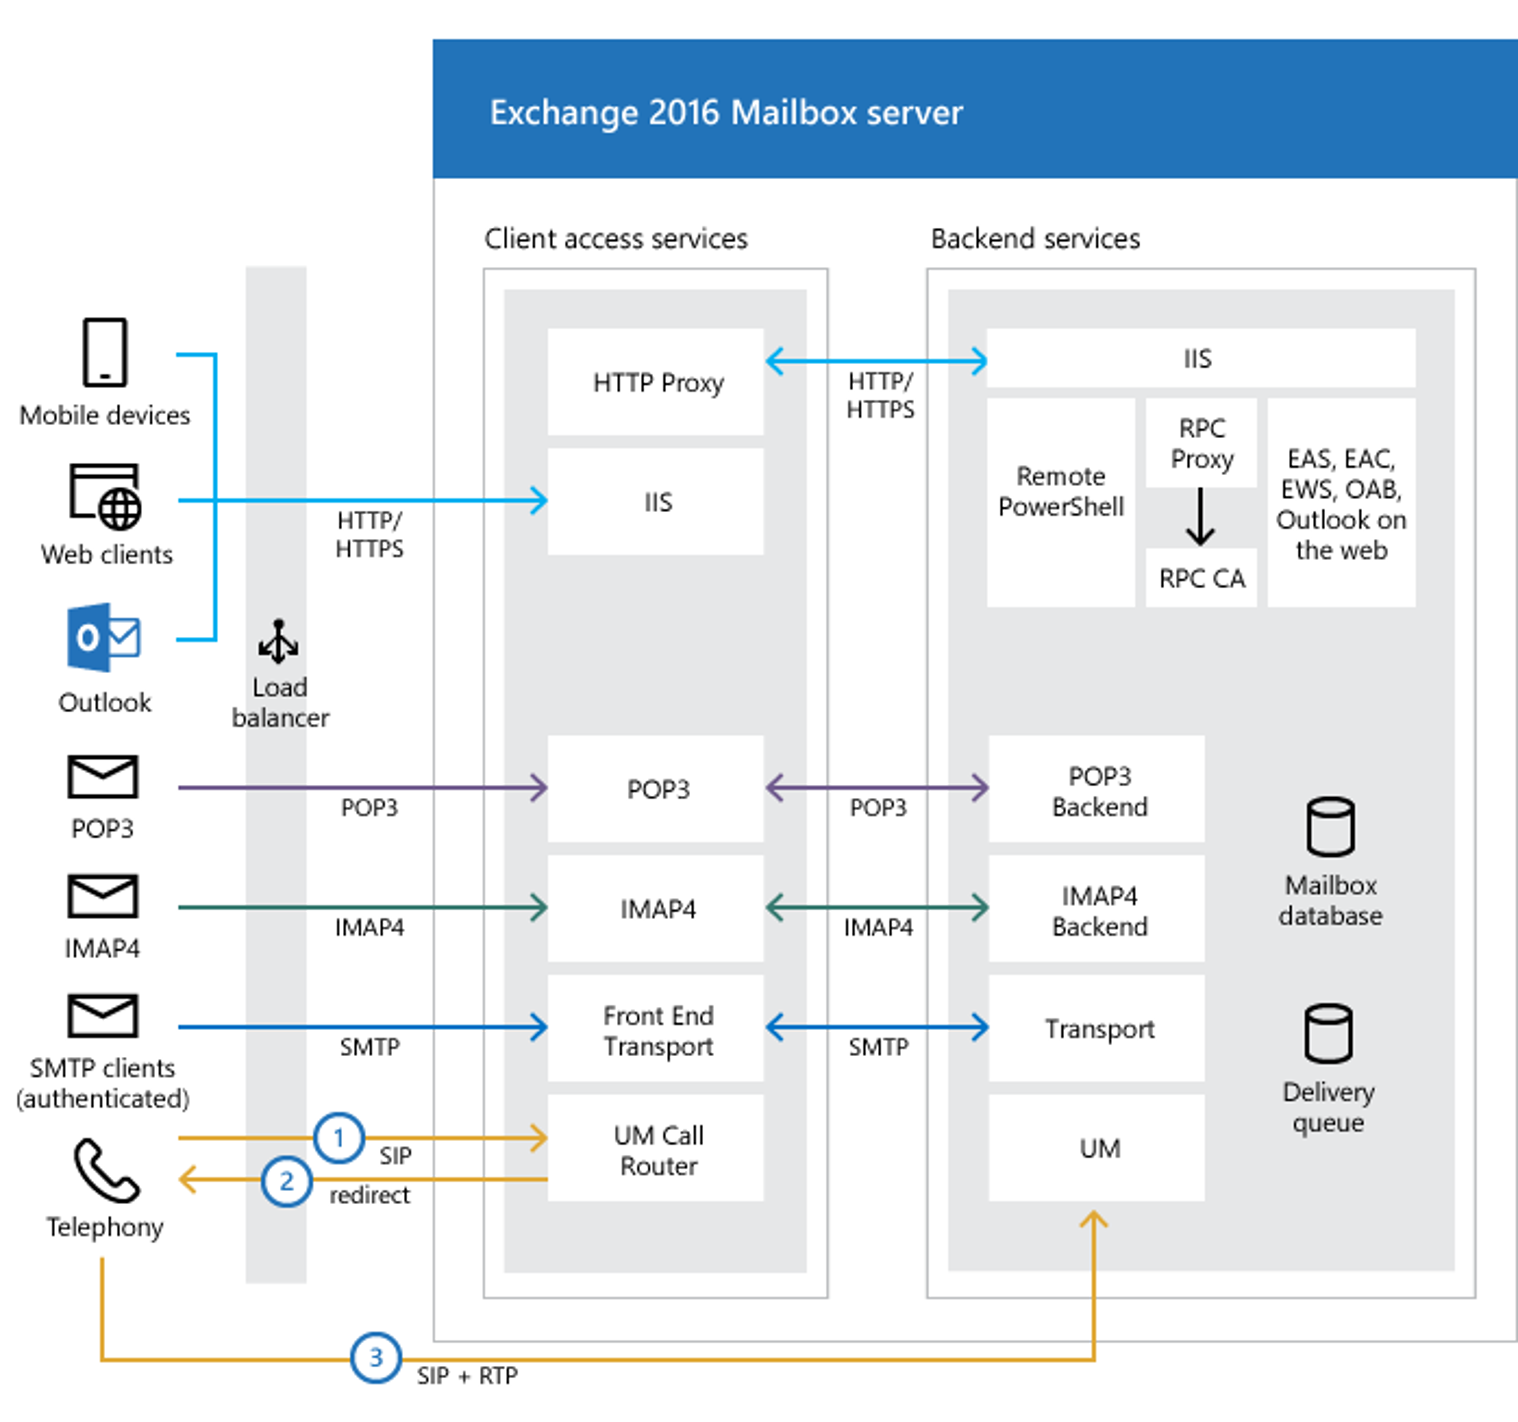
All client connections are handled by the frontend, which proxies any given request to the backend according to the request. Here in this scenario the specific requests made to the frontend, like URLs, are dealt with by backend services.

Exchange Mailbox Server

A ProxyNotShell attack targets the Remote PowerShell service, which in this case is the backend service that is targeted. It is known this kind of vulnerability is referred to as an SSRF (Server-Side Request Forgery) vulnerability.

The CVE-2022-41082 vulnerability has been exploited by ransomware operators in order to execute arbitrary commands on compromised servers using Remote PowerShell.

OWASSRF PoC exploit leak

POC code for an exploit method based on Play ransomware logging was currently under development by CrowdStrike security researchers.

A recent discovery has shown that an attacker has downloaded all of the tools from an open repository, uploaded them in a MegaUpload link, and made them accessible to the public via the Twitter site.

CrowdStrike researchers replicated the log files generated in recent Play ransomware attacks using a Python script from the leaked toolkit, named poc.py, that was included in the leaked toolkit.

Recommendations from CrowdStrike

Here below we have mentioned all the recommendations offered by CrowdStrike:-

  • Since the URL rewrite mitigations for ProxyNotShell do not function against this exploit method, organizations should apply the Exchange patches of November 8, 2022. 
  • The KB5019758 patch should be applied as soon as possible, but if this cannot be done, then you should disable OWA until you are able to apply it.
  • Make sure to disable remote PowerShell for non-administrative users in accordance with Microsoft’s recommendations.
  • Implement the use of advanced endpoint detection and response (EDR) solutions on each and every endpoint.
  • Utilize the script developed by CrowdStrike Services to check for signs of exploitation on Exchange servers visible in IIS logs and Remote PowerShell logs.
  • Take into account application-level controls, such as firewalls for web applications, as well as system-level controls.
  • Ensure that the X-Forwarded-For header in the HTTP request has been configured to log the true IP address of the external proxy server.

Secure Web Gateway – Web Filter Rules, Activity Tracking & Malware Protection – Download Free E-Book

Adblock test (Why?)


You may be interested in:
>> Is a Chromebook worth replacing a Windows laptop?
>> Find out in detail the outstanding features of Google Pixel 4a
>> Top 7 best earbuds you should not miss

Related Posts:
>> Recognizing 12 Basic Body Shapes To Choose Better Clothes
>>Ranking the 10 most used smart technology devices
>> Top 5+ Best E-readers: Compact & Convenient Pen
Read More
  • Share This:  
  •  Facebook
  •  Twitter
  •  Google+
  •  Stumble
  •  Digg

Hackers Use New BrasDex Android Malware to Steal Users’ Banking Details

 December 21, 2022     No comments   

New BrasDex Android Malware

A new Android trojan called BrasDex has been identified as the work of the same threat actors responsible for the Casbaneiro malware that targets Windows banking systems. 

The security analysts at ThreatFabric recently spotted an ongoing multi-platform campaign in which Brazilian users have been observed to be targeted as part of this malware (BrasDex) attack.

Complicated Keylogging capabilities are built into BrasDex to exploit the Accessibility Services in an attempt to extract and acquire credentials specifically from:-

  • A set of Brazilian-targeted apps
  • A highly capable Automated Transfer System (ATS) engine

BrasDex Android Malware Stealing User Data

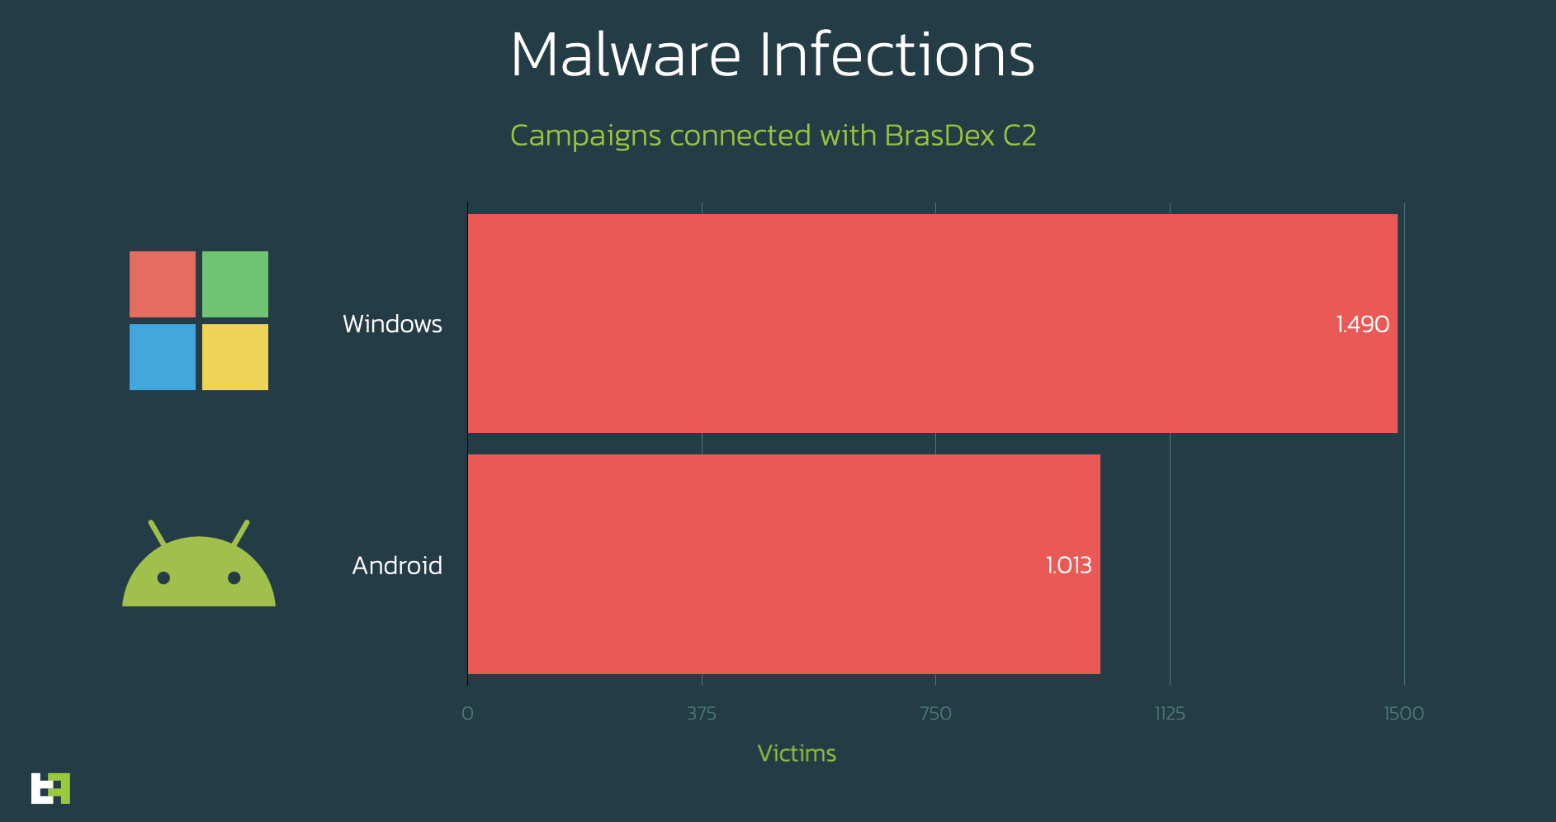
Casbaneiro is also being controlled via the C2 infrastructure that is being used in conjunction with BrasDex. Brazil and Mexico are the two countries that have also recently experienced the same problems with their banks and cryptocurrency services.

Malware Infections

This malware has been active for over a year now and initially misrepresented itself as an Android setting application to specifically target Brazilian banking apps.

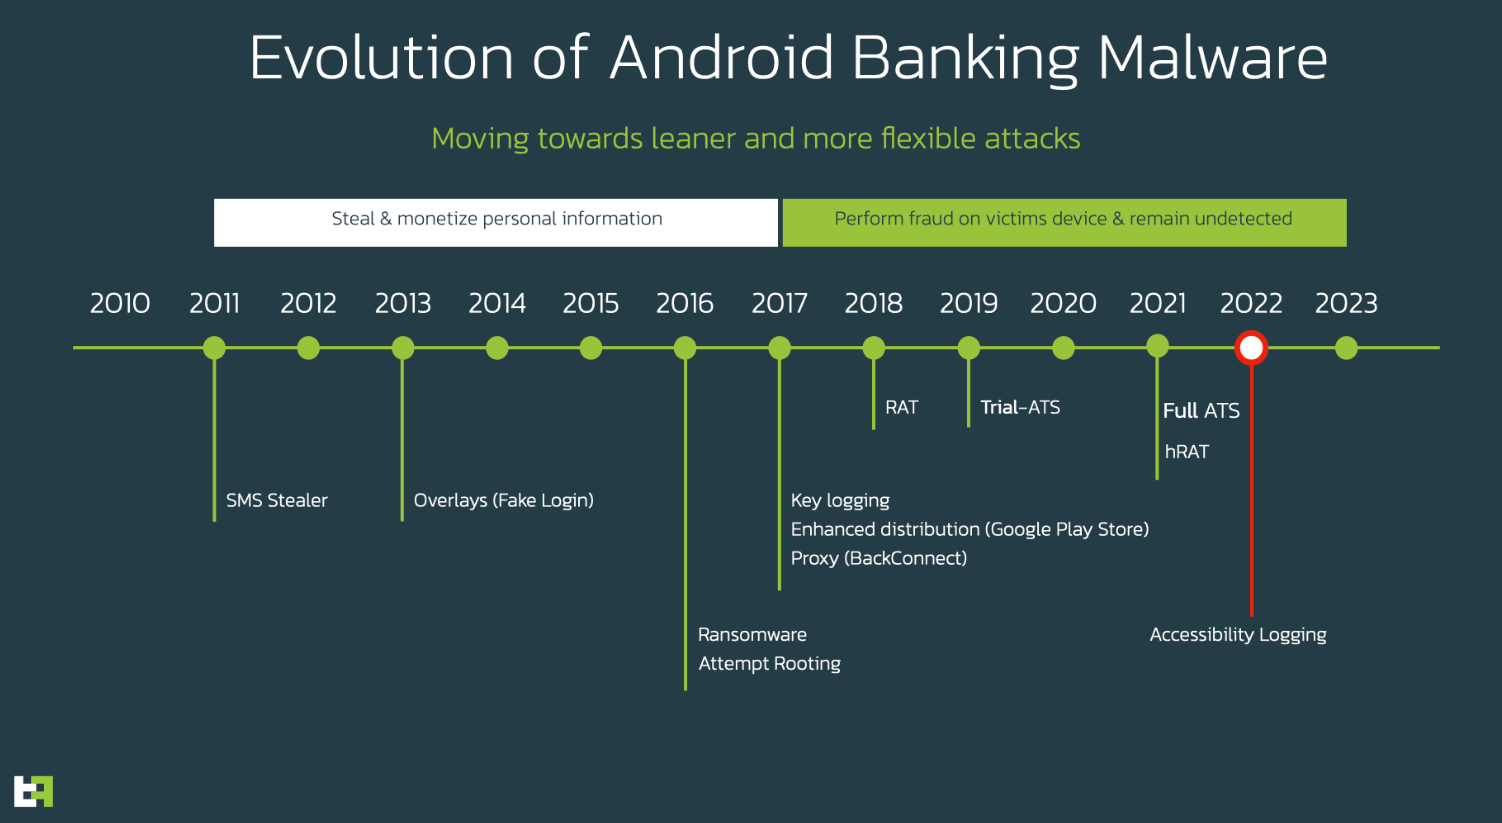
The various malware families have begun to abandon the use of overlays for a more lean and flexible solution, which does not require a continuous update or additional data to be downloaded, as they are more efficient.

Evolution of Malware

It is becoming more and more common for malware families to incorporate accessibility logging into their malware designs in order to extract logging credentials and other personal information from victims infected by the malware.

ATS (Automated Transfer System) capabilities are one of the main reasons that make BrasDex stand out from many other malware families.

BrasDex Capabilities & Panel

Here below we have mentioned the capabilities of BrasDex:-

  • Keylogging
  • ATS

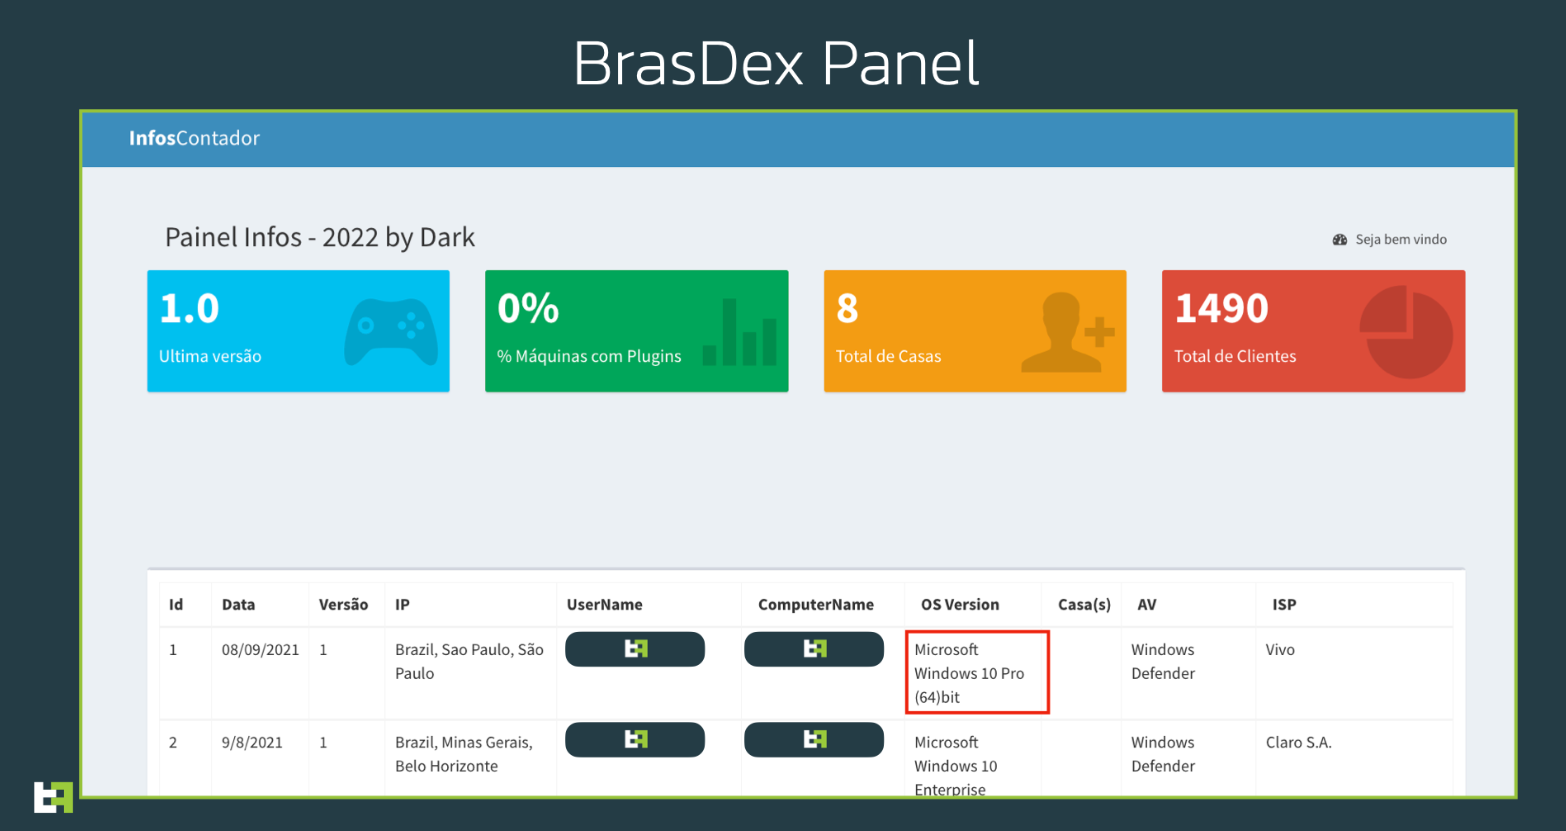
As ThreatFabric investigated this malware family, they were also able to get some visibility into the Panel hosted on the C2 server, which was an important discovery.

The panel contains multiple pages and other important information like:-

  • List of infected devices
  • List of service providers
  • List of the device models
  • List of the Android version
  • Logs obtained from the infected devices
Malware Control Panel

Targets Attacked

Specifically focused on the Brazilian market, BrasDex is one of the most well-known malware families. In order for the malware to operate on Brazilian devices only, test checks are included in the malware itself. 

It did this by performing a programmatic check on the SIM card used by the device to ascertain that its SIM is operating in Brazil, after which it complete all its desired operations and then configure the device properly. 

However, the malware automatically shuts down and abandons all the communicating channels to its C2 server, if it detects that the SIM card on the device is from anywhere else.

There may be some unknown problem with the Pix payment system within the Brazilian banking ecosystem causing this hard dedication to a single market.

In 2020, Pix was introduced and has been one of the fastest payment systems ever created by the Brazil Central Bank. By knowing a user’s identifier, it is possible for a user to transfer payments to another user via Pix.

There is no doubt that BrasDex and Casbaneiro are two of the most dangerous malware families available today. A large number of Android and Windows users can be targeted in broad daylight by the actor behind them.

On the very first border of the transaction, there is an urgent need for an effective solution to detect suspicious behavior during the transaction as well as to identify the threats present on the device of the customer.

Secure Web Gateway – Web Filter Rules, Activity Tracking & Malware Protection – Download Free E-Book

Adblock test (Why?)


You may be interested in:
>> Is a Chromebook worth replacing a Windows laptop?
>> Find out in detail the outstanding features of Google Pixel 4a
>> Top 7 best earbuds you should not miss

Related Posts:
>> Recognizing 12 Basic Body Shapes To Choose Better Clothes
>>Ranking the 10 most used smart technology devices
>> Top 5+ Best E-readers: Compact & Convenient Pen
Read More
  • Share This:  
  •  Facebook
  •  Twitter
  •  Google+
  •  Stumble
  •  Digg

How to Lose $13 of Users’ Funds (As a Blockchain Developer)

 December 20, 2022     No comments   

The gov says we are not in recession, but at the same time, we hear about skyrocketing inflation, interest rate increases, and layoffs in almost every sector of the economy.

Despite crypto and TradFi being impacted the most severely, many companies are still building their tokens, protocols, and DeFi products. Are you one of them?

Today, I will be speaking on data types, and hold on. I have something very important to say. You might picture me as a 60+-year-old professor from MIT torturing students with lectures about subjects that no longer matter. But that’s not true.

Data types are still important, and neglecting them leads to serious consequences. I will try to briefly go through all potential issues and address them so you don’t find the 8 minutes you spend on reading this article wasted.

Modern languages like JavaScript and Python are using “duck typing” to determine the type of variable. If we assign this sort of formula a = 2 + 2 to a variable, the language interpreter knows it is dealing with numbers, and it will perform mathematical operations on this literal.

The duck typing can be explained by this sentence: “If it walks like a duck and it quacks like a duck, then it must be a duck”. When you look closer into the meaning of it - it makes perfect sense. If literal has letters and numbers, it must be a string, and that’s clear. But what if it has numbers?

Is it a boolean, integer, decimal, float, or date. In most cases, your language interpreter will handle types in the correct way. The problem starts when your program needs to run (even simple) equations on large numbers.

“If it walks like a duck and it quacks like a duck, then it must be a duck”, right? Actually it’s not.

Ethereum Denominations in a Nutshell

In the next paragraphs, I am referring to Ethereum common denominations - wei and gwei. Let me briefly introduce you to them so we speak the common language.

The smallest denomination is 1 wei, and 1 ether equals 1,000,000,000,000,000,000 Wei (18 zeros). I repeat - 18 zeros. It is hard to wrap our minds around such large numbers but they make a difference and matter a lot.

The next common denomination is 1 gwei. 1 ether equals 1,000,000,000 gwei (9 zeros). Gwei is more bearable for humans - in the end, everybody wants to be a millionaire, right? (wink, wink)

Let’s sum it up - 1 ether equals:

  • 1,000,000,000 gwei (9 zeros)
  • 1,000,000,000,000,000,000 wei (18 zeros)

Technical note: Ethereum has two layers - the execution layer and the consensus layer. The execution layer is using wei to represent ether values, and the consensus layer is using gwei. If you are a blockchain developer, you need to learn to interact with both.

Real-World Example: Stakefish’ tip and MEV Pool

I am a software engineer at stakefish. I’m responsible for building our DeFi products palette, and one of the most recent ones is our tip and MEV pool for Ethereum.

Starting from September 15, 2022, all validators are eligible for transaction tips and can participate in MEVs to earn additional rewards. Transaction tips and MEVs are earned when the validator proposes a new block.

We decided to build a smart contract that collects all rewards into a common vault and allows user to claim their share from it. I am not trying to advertise our product, but I need to set the context of this article.

If you are more interested in this product, you can read more here. I’m not selling you anything besides my experience.

As I mentioned, we have a smart contract that receives transaction tips and MEV rewards earned by validators. It means our smart contract has a fairly large balance. It is 963+ ether now ($1.1M), and we have 8671 validators contributing to it.

The critical part responsible for synchronization between Ethereum execution and the consensus layer is Oracle. It is a very important system that allows us to determine what validators are contributing to the pool.

The oracle is written in Python, but it could be written in JavaScript - the problem remains unchanged, and I will prove it soon.

Let’s deep dive into the code!

Why Data Types Matter

The balance of the smart contract equals 963,135,554,442,603,402,422 wei (963 ether) now. This number isn’t only hard to understand for humans but also for computers (language interpreters to be exact). Let’s check JavaScript:

const vault_balance = parseInt("963135554442603402422")
console.log(vault_balance)
// 963135554442603400000 (lost 2422 wei in total)

I only casted the balance from string to int, and I am already 2422 wei short. We didn’t run any equation yet.

The smart contract balance is so high thanks to many validators contributing to it. Now, let’s calculate what the average validator share of contract’s balance now:

const vault_balance = parseInt("963135554442603402422")
const validator_count = 8671

const avg_validator_contribution = vault_balance / validator_count
// 111075487768723730 (lost 7 wei per validator)

The average share is 0.111 ether. But this amount isn’t correct - we are actually 7 wei short. It is 60,697 wei in total (7 wei times 8671 validators). I will show the correct number later on.

Proceeding further down the rabbit hole of losses - let’s calculate the total amount of rewards per given validator. Have in mind that the user needed to deposit 32 ether to start a validator, so I will deduct it from the validator balance.

And I will take as an example one random validator contributing to the smart contract that has a balance of 32.779 ether.

const vault_balance = parseInt("963135554442603402422") // (lost 2422 wei)
const validator_count = 8671
const avg_validator_contribution = vault_balance / validator_count // (lost 7 wei)

const initial_deposit = parseInt("32000000000000000000")
const validator_balance = parseInt("32779333896000000000")

const total_validator_rewards = validator_balance - initial_deposit + avg_validator_contribution
// 890409383768723700 (lost 23 wei per validator)

The total rewards earned by this validator equals 0.8904 ether, but this value isn’t accurate as well. At this moment, we miscounted for 199,443 wei in total (23 wei times 8671 validator). As you can see, this way of calculating numbers isn’t sustainable.

What Goes Wrong?

There are two problems with the code above:

  • In JavaScript, the maximum safe value for integers equals 2^53 - 1 only. It means it can handle up to 9007199254740991 wei (0.009 ether)
  • Technically, we could have used BigInt but we would have problems with division. We would end up with “floating” values. The floats are the root of all evil in finance because they are approximate. It means they lose precision. We need to use decimals. (The main difference between decimal and float is that decimal stores exact value and float approximates.)

If you ever had done any Ethereum-related coding in JavaScript, you must’ve heard about ethers.js. This library contains all the necessary utilities to interact with the blockchain. To fix the issue above, we will use one of the tools called BigNumber that supports extremely large numbers and handles decimals in the right way.

Let’s do it!

const vault_balance = BigNumber.from("963135554442603402422") // no loss
const validator_count = BigNumber.from(8671)
const avg_validator_contribution = vault_balance.div(validator_count) // no loss
// 111075487768723723

const initial_deposit = BigNumber.from("32000000000000000000")
const validator_balance = BigNumber.from("32779333896000000000")

const total_validator_rewards = validator_balance.sub(initial_deposit).add(avg_validator_contribution)
// 890409383768723723

As you can see, now we ended up with the accurate number. How do I know this is actually the right number? I will repeat the same exercise in Python to prove that I’m right.

Let’s Try It in Python

Python supports long integers, so the values will not get suddenly cut as we have seen in JavaScript. Unfortunately, it still determines all floating numbers as floats by default:

vault_balance = int("963135554442603402422") # no loss
validator_count = 8671
avg_validator_contribution = vault_balance / validator_count
# 111075487768723728 (5 wei too much)

initial_deposit = int("32000000000000000000")
validator_balance = int("32779333896000000000")

total_validator_rewards = validator_balance - initial_deposit + avg_validator_contribution
# 890409383768723712 (lost 11 wei)

Wondering where exactly it lost precision? The division casted avg_validator_contribution to float instead of decimal. The correct snippet would look like that:

vault_balance = Decimal("963135554442603402422")
validator_count = Decimal(8671)
avg_validator_contribution = vault_balance / validator_count
# 111075487768723723

initial_deposit = Decimal("32000000000000000000")
validator_balance = Decimal("32779333896000000000")

total_validator_rewards = validator_balance - initial_deposit + avg_validator_contribution
# 890409383768723723

Now, the values returned by Python and JavaScript are exact. Check on your own!

These sorts of losses are marginal, and they can be easily missed. Often, we find out about them when they compound over time and grow to significant numbers.

Situations like that always give headaches, not only to developers but also to other departments such as finance or legal. You should always test your formulas, and never use nice round numbers to do so!


It would mean the world to me if you follow me on Twitter. I am focusing my activity on software engineering and blockchain. I am open-sourcing most of my work, so you might want to check my GitHub.

L O A D I N G
. . . comments & more!

Adblock test (Why?)


You may be interested in:
>> Is a Chromebook worth replacing a Windows laptop?
>> Find out in detail the outstanding features of Google Pixel 4a
>> Top 7 best earbuds you should not miss

Related Posts:
>> Recognizing 12 Basic Body Shapes To Choose Better Clothes
>>Ranking the 10 most used smart technology devices
>> Top 5+ Best E-readers: Compact & Convenient Pen
Read More
  • Share This:  
  •  Facebook
  •  Twitter
  •  Google+
  •  Stumble
  •  Digg

We Need an Open Internet, Web3 Has Been Reduced to a Marketing Term

 December 19, 2022     No comments   

This post is mainly intended as a comment on Jack Dorsey's push for a native internet protocol for social media. The so-called "Twitter Files" is a part of the story.

In general, I try to stay out of politics and report as neutrally as I can about technology's impact on society, and vice versa. However, Twitter Files have become a highly polarizing topic.

At the end of this piece, you can find excellent articles addressing them from independent journalists across the political spectrum.

Twitter Files and the political component of content moderation

Twitter Files are a series of "Twitter🧵" initiated by Elon Musk where three independent journalists - Matt Taibbi, Bari Weiss, and Michael Shellenberger - report on internal documents from the former Twitter administration. Overall, Twitter Files provide evidence of how content was moderated, stories were suppressed, and accounts were banned and shadow-banned according to either a left-leaning political agenda or by direct orders from the US government.

In regards to the political aspect, Twitter Files confirm accusations that US conservatives have made against Twitter for years. Jack Dorsey even admitted in 2018 that Twitter employees share a largely left-leaning bias although they were not instructed to act according to political ideology or viewpoints.

Critics could make a good case that Twitter under the new "Musk regime" is also biased. For example, a number of prominent journalists recently had their accounts temporarily suspended without any explanation. Matt Binder, one of the suspended journalists, wrote a piece about the incident here. As did Taylor Lorenz from Washington Post who was suspended this weekend here. The suspensions appear arbitrary, directed at journalists who have spoken disfavourably against Musk. When confronted with the fact, take a look at Musk's outlash here.

It sets a dangerous precedence when freedom of speech becomes politicized. Overall, I think Peter McCormack, host of "What Bitcoin Did", makes a good point:

While freedom of speech should in theory apply equally to everyone, content moderation is not completely neutral. Given a large enough sample size, there will always be edge cases that could be determined in either direction, and over time biases will show. In short, there is a political component to content moderation, while freedom of speech should apply equally to everyone. And as long as there is a central point of control or a "single point of failure" interference from governments and lobbyism is probably hard to avoid.

In the latest edition of Twitter Files, "Part Six TWITTER, THE FBI SUBSIDIARY", Matt Taibbi writes about how the former Twitter Trust and Safety Chief routinely acted upon requests from the FBI to take down content. This can hardly come as a surprise! To anyone just remotely familiar with the Snowden revelations or FISA Section 702 - which authorizes extensive surveillance of foreign citizens - Taibbi's post is a large nothingburger.

Jack Dorsey's push for open social media

Last Tuesday, Jack Dorsey published a blog post on the Twitter-affiliated newsletter platform Revue where he addresses the "Twitter Files" and suggests "how to fix the identified issues". Interestingly enough, Revue announced that they would shut down the platform just one day after Dorsey's post. Seems like a strange coincidence.

Dorsey starts by uplisting three principles he believes a social media platform should adhere to:

1.    Social media must be resilient to corporate and government control.

2.    Only the original author may remove content they produce

3.    Moderation is best implemented by algorithmic choice.

Twitter doesn't reflect these principles and Dorsey takes full responsibility for it:

This is my fault alone, as I completely gave up pushing for them when an activist entered our stock in 2020.

Here, Dorsey is likely referring to the hedge fund Elliott Management Corp. which bought a majority share in Twitter that year.

In regards to Dorsey's first principle - that social media must be resilient to corporate and government control - he writes:

Of course governments want to shape and control the public conversation, and will use every method at their disposal to do so, including the media. And the power a corporation wields to do the same is only growing. It's critical that the people have tools to resist this, and that those tools are ultimately owned by the people. Allowing a government or a few corporations to own the public conversation is a path towards centralized control.

Dorsey's second principle - that only the original author may remove content they produce - is controversial and probably hard to implement. At least from a legal standpoint. For example, Germany has passed a law that orders Facebook, Google, and Twitter to remove hate speech and "obviously illegal content" within 24 hours or face a fine of up to €50 Million.

Dorsey's third principle - that moderation is best implemented by algorithmic choice - is about giving user's more of a choice over what type of content they see. Users could be allowed to customize the filters of their algorithmic feeds, or alternatively choose between different "ranking providers". If you'd like to learn more see Stephen Wolfram's essay here.

As a whole, Dorsey's principles allude to more decentralization, censorship resistance, transparency, and user control on social media. These are all key properties of Bitcoin. Not a coincidence since Dorsey is a keen Bitcoin supporter. The Web3 movement strives for the same values but, intentionally or not, Dorsey refrains from using ubiquitous marketing terms such as Web3 or crypto.

Instead, Dorsey calls for a free and open protocol for social media and points to projects such as AT Protocol, Mastodon, and Matrix as competing candidates to become a standard like HTTP or SMTP.

Web3 Vs the Open Internet

The term "Web3" is often associated with new NFT collections and discounts on token sales. Crypto opportunists and salespeople want to jam it down our throats. However, in the wake of Twitter's Musk-induced existential crisis, there seems to be an organic push for a more open internet. Which is indeed the underlying philosophy of Web3. But the idea of a more open internet extends far beyond blockchain and crypto - although blockchain technology is likely a part of the solution. An open internet gives the user the power of choice between many different platforms, instead of complete dependency on a few, all-powerful ones.

Noah Smith writes in The internet wants to be fragmented:

People call Twitter an indispensable public space because it's the "town square", but in the real world, there isn't just one town square, because there isn't just one town. There are many. And the internet works when you can exit — when you can move to a different town if you don't like the mayor or the local culture.

It will be interesting to see to what extent Elon Musk's God complex and the divisiveness on Twitter will draw users toward other platforms. And if there will be a loud mass exodus at once, or if people will leave quietly through the backdoor over time like teens have done with Facebook. Either way, Twitter's competitors are eyeing an opportunity to capitalize on the chaos, and it seems like the thick shackles on people's attention and data are finally loosening up

Here are some excellent articles addressing "Twitter Files" from independent journalists across the political spectrum:

Mike Solana: The Fifth Estate

Abigail Shrier: Real Time Doxxing and the Littlest Musk

Matt Binder: Twitter has a freedom of speech problem and it's Elon Musk

Also published here. 

L O A D I N G
. . . comments & more!

Adblock test (Why?)


You may be interested in:
>> Is a Chromebook worth replacing a Windows laptop?
>> Find out in detail the outstanding features of Google Pixel 4a
>> Top 7 best earbuds you should not miss

Related Posts:
>> Recognizing 12 Basic Body Shapes To Choose Better Clothes
>>Ranking the 10 most used smart technology devices
>> Top 5+ Best E-readers: Compact & Convenient Pen
Read More
  • Share This:  
  •  Facebook
  •  Twitter
  •  Google+
  •  Stumble
  •  Digg

Top 10 Best Malware Removal Tool 2023

 December 19, 2022     No comments   

Top 10 Best Malware Removal Tool 2020

Malware removal tool helps to remove the dangerous malware from your personal computer to protect from hackers and prevent future attacks.

Today the most essential thing is to have security on your PC or laptop, as you never know when the cybercriminals will attack.

This implies that you don’t only need Antivirus software, but also a malware removal tools as well.

Well, there is a vast difference between adware and spyware, they are not viruses.

Thus, determining that your device has been affected with malware is far from ideal, and the method to remove anything consumed can be exhausting. 

Well, some exertions have even been designed to be as challenging to remove.

Therefore, Malware has become a common problem, since it’s more evident than ever to pick up malware, even when you think your internet performance isn’t hazardous, that’s why malware elimination tools exist.

The best malware removal tools will exceed at virus removal and trafficking with spyware.

Therefore, we analyzed various malware removal tools for Windows and Mac computers. But some malware can go undetected for a long time; we can say even years. 

Hence, the Slingshot was in time discovered by Kaspersky Labs after it gets affected and huddled inside routers for six years without any remarking.

Thus its extremely advanced form of malware; therefore, it able to collect desktop activity and clipboard data, as well as collect screenshots, network data, keyboard data, passwords, and data from USB devices as well.

However, malware is not something that you want lagging around your PC, so immediate removal is the best way to eliminate the risk.

Luckily, there are many types of malware removal tools, and several of them are free, although some are paid upgrades.

So, if you want to remove something particular , here are our top selection to keep your system free of malware.

So, now we will move to our list of best anti-malware removal tools. So, in this list, we have selected the top 10 anti-malware tools among all, which will simply help you to eliminate the risk.

What is Malware?

The term malware is small for ill-disposed software, and it applies to completely any program or method whose primary goal is harmful, even illegal.

The most advanced form of malware was the computer virus, the name for a memorandum that affects other programs with its code, and reproduces when the infected application operates.

Well, several viruses had no wicked payload; they just assisted in showing off the coder’s skills. Thus, a virus flows when someone originates from the infected program.

However, due to a coding error, it dropped thousands of servers and obtained its creator a felony conviction.

Modern malware coders are way exceeding the “look at me!” approach of those early virus authors.

Therefore, the Trojans that communicate your private data are one kind of spyware.

Moreover, there are other varieties of spyware focus on tracing your web-browsing practices or notices your direction of computer.

If this sort of attack goes onto your computer, you’ll find that all your necessary files have been encrypted.

Thus the culprit of the attack will cheerfully decrypt them for you, only if you will pay the payment or ransom.

Most dangerous among all, yes, it’s one of the most troubleshooting problems, which creates a lot of difficulties, and the victim has to suffer from high losses.

Why Do You Need Malware Protection?

Now some of you might be thinking that why it’s necessary to use a malware protection tool? Well, with the help of your computer software, you create and communicate.

Several users generally use the term wetware to explain the imaginative spark that notifies what you say, write, or draw.

However, malware can have severe damaging approaches to all three other varieties of “ware.”

Thus, it can clasp up or damage your hardware, destroy or spoil your software, and give you difficulty in performing your daily basis task.

Therefore, in that case, you require security against malware in the form of an antivirus efficiency at a point. And running without security makes no sense because you never know when your system is going to get attacked.

Malware protection resolutions come in all volumes. Despite the word “virus” in the title, antivirus efficiency intends to defend against all types of malware.

Hence, full-scale protection sets extend security to cover such things as spam filtering and parental control.

Furthermore, several malware removal tool work beside your main protection to accommodate added security upon specific threats, for example, ransomware.

Thus, before exploring the different varieties of protection available, let’s know about what is the difference between anti-virus and anti-malware.

What is the Difference Between Anti-Virus and Anti-Malware?

The main objective of anti-virus software is to implement protection. This software application is generally used to restrict virus-laden files from being download on your system.

Besides that, it operates to stop the virus from stimulating in case if it somehow gets its way to your system.

While on the other hand, anti-malware software is also known as a malware removal tool, and it is somewhat different in how it operates.

Whereas anti-virus software is all about restraint, thus anti-malware software seems to root out and finishes the malware that is now downloaded and activated on a system.

But there are several similarities between these two types of software. Thus every expert recommends utilizing both to increase the protection and the security layer of your PC or laptop.

So, like the Adware removal tool, now without wasting much time let’s get started and simply explore the whole list that we have mentioned below.

Best Malware Removal Tool 2023

  • Malwarebytes Anti-Malware
  • Microsoft Malicious Software Removal Tool
  • IObit Malware Fighter
  • Spybot Search & Destroy
  • Zemana Antimalware
  • GridinSoft Anti-Malware
  • Adaware Antivirus Free
  • STOPzilla
  • SUPERAntiSpyware
  • Emsisoft Emergency Kit

1. Malwarebytes Anti-Malware

Malwarebytes Antimalware

At first, we have the Malwarebytes Malware Removal Tool in our selection, well, if you assume a malware infection, then Malwarebytes Anti-Malware should be your first selection.

The most amazing part of this tool is that it’s updated daily, so you can trust it to recognize and eliminate new threats the moment they emerge.

When you install Malwarebytes Anti-Malware for the first time, you will get a 14-day trial of the premium version, which covers preventative tools like real-time scanning and special protection from ransomware.

Then, after two weeks, it returns to the original free version. This has to be stimulated manually, but it is still a top-notch security tool.

Hence, we suggest that running this software at least once in a week to review or any virus has been entered that you haven’t marked, or if you see that your web browser has abruptly started acting oddly.

Recently, Malwarebytes has already bought Adwcleaner, which targets and eliminates bothersome programs that capture your browser by turning your homepage, resetting your default search engine, or attaching unwanted toolbars.

Well, this software is free, and besides Anti-Malware, it is an excellent addition to your protection toolkit.

2. Microsoft Malicious Software Removal Tool

Microsoft malware removal tool

In second no. we have the Microsoft malicious software removal tool. Its also known as the Windows Malicious Software Removal Tool (MSRT) well it’s a free anti-malware tool developed by the tech giant Microsoft.

The MSRT (Microsoft Malicious Software Removal Tool) is frequently downloaded with automated updates to run beside the built-in Windows Defender AntiVirus.

But, for those users who prefer the automatic updates regularly turned-off, you can download the software straight. 

As the MSRT gets its update once a month to allot with the most current threats, namely professed by viruses, worms, and trojans.

In case if it doesn’t disclose anything, then it operates in its quiet mode, but if it does an aircraft alert, it will resemble stating that malware has been identified and demands to be removed.

Well, if you strive to eliminate any problems with the MSRT, then you can also try the Microsoft Safety Scanner, which is also accessible as a download, and this is also created by Microsoft to identify and eliminate malware from Windows computers, but it is actually planned or designed to run in the assistance of the Microsoft Malware Removal Tool.

This image has an empty alt attribute; its file name is button_download.png

3. IObit Malware Fighter

IObit Malware Removal Tool

Next, we have the IObit Malware Removal Tool. It has another part that is the malware fighter 6.2, it is performance optimization software, which combines Driver Booster, Advanced Systemcare, Smart Defrag, Password manager, and many more.

This one is a protection combination that intends to preserve random web surfing from the newest ill-disposed threats like ransomware and avdware.

Moreover, it exposes all kinds of malware, and not only that even it also offers different types of scans that are moderately handy as well.

Apart from all these things, it has an extensive database of threats that get updated regularly.

Moreover, it also informs the users about the ransomware through a notification in advance, which is really good.

This image has an empty alt attribute; its file name is button_download.png

4. Spybot Search & Destroy

Malware Removal Tool
Spybot search & destroy

Next, we have the Spybot search & destroy. Well, this software offers a counterproductive resolution to spyware and adware by identifying and eliminating malware from a Windows system.

Hence, Spybot launched the first adware in the industry by choosing it out soon after founding in 2000.

Moreover, it acts as a protector against future attacks by wicked software.

Thus this software is often followed by experts and advanced users who have exceptional knowledge of malware. 

Well, the expert states that Spybot automatically identifies adware networks and their struggles at redirection, registry adjustments, differences in browser arrangement.

Thus its free edition covers features like anti-spyware, anti-adware, adware removal tool, cookie cleaner, program cleaner.

Not only this, it’s full version is comparatively cheaper in contrast to another antivirus software available.

Lastly, it also offers immunization against future malware attacks as well.

This image has an empty alt attribute; its file name is button_download.png

5. Zemana Antimalware

Malware Removal Tool
Zemana Antimalware

After that, we have the Zemana Malware Removal Tool. Its mainly developed to run a full scan upon advising, as Zemana operates by identifying and collecting file fingerprints on a cloud server after removing them from your computer.

Well, this free anti-malware program practices negligible hard drive space and can be used concurrently with other related tools.

Zemana uses few resources and yet manages to do the full scans.

Though it was never developed to be the first line of protection, but, this anti-malware is very useful to remember other antivirus software.

Well, every user thinks it’s very helpful in the sense that it seamlessly works with other antivirus tools and offers all the actions to fulfill their requirements.

This image has an empty alt attribute; its file name is button_download.png

6.GridinSoft Anti-Malware

Malware Removal Tool
Gridinsoft anti-malware

Then we have the Gridinsoft anti-malware too. Well, this antimalware app by Gridinsoft company works on all popular versions of Windows OS, and it is excellent to remove spyware, adware, PUPs, etc.

The main obstacle in its free version is that it solely scans a computer – for extraction functionality, one has to pay.

After the scan, all warnings are grouped, and there’s information, a way to it on PC, and a threat level to all threats or uncommon programs.

An excellent malware scanner and Malware Removal Tool that does not take full space on the user’s PC or device. 

Hence, the administrator supports a typical business strategy: that is used for free to browse and pay to extract and clean.

Therefore it provides various types of scans like scan log, extra tools and much more.

Not only this even it also has a portable Trojan-killer version as well which is available for download.

This image has an empty alt attribute; its file name is button_download.png

7. Adaware Antivirus Free

Malware Removal Tool
Adaware Antivirus Free

Next, we have the Adaware Antivirus Free. It is another excellent option if you’re developing a Malware Removal Tool from the ground up.

It combines a virtual environment where questionable programs can be examined to see if they work like malware or not.

This means you’re always shielded from new malware – even if you’re the very initial person to be affected, and the wicked program isn’t yet in Adaware’s database of known warnings. 

The malware can then be harmlessly checked and removed. Well, all this occurs quietly in the background and can be interrupted temporarily if you want your processor’s full potential for a gaming session.

Moreover, Adaware Antivirus Free can scan downloads before you install them, thus helps in preventing malware infection in the first place by filtering their most obvious point of entry.

Hence, if you’re studying for a way to boost your current antivirus software, Adaware’s installer lets you pick a version without real-time scanning that won’t contrast with other antivirus tools.

This image has an empty alt attribute; its file name is button_download.png

8. STOPzilla

Malware Removal Tool
STOPzilla

After that we have STOPzilla. It’s one of the most anticipated Malware Removal Tool, and it has earned various awards and rave reviews. Practicing a thorough database, STOPzilla Malware Removal Tool lets users effortlessly eliminate malware and spyware from their Windows computer to keep private data safe.

Its all because of the Cloud Technology, that STOPzilla Antimalware presents comprehensive protection while using minimum CPU resources, even when working in combination with other security software, simply enabling your computer to stay as quick as possible.

Not only this, its counterparts antivirus solutions to implement the most comprehensive protection attainable against the range of computer security threats.

This image has an empty alt attribute; its file name is button_download.png

9. SUPERAntiSpyware

SUPERAntiSpyware

Then we have SUPERAntiSpyware, it’s one of our top pick for the most reliable malware removal tool that’s able to stop spyware and malware.

This tool basically trains in spyware, but it can also manage a difference of other threats, including rootkits and ransomware.

Well, SUPERAntiSpyware is created to work in accordance with your antivirus, especially targeting spyware, adware, keyloggers, and other warnings to your data.

It’s also able to defend your files against ransomware, which is created to hijack your data unless you pay the attacker to deliver it. 

However, the free version of SUPERAntiSpyware begins with the same daily updates as the paid version, guaranteeing that you’re always guarded against the latest threats.

The only disadvantage of this tool is that you have to check for updates manually. Furthermore, it is only available for Windows, but it is agreeable with every version of the operating system following Windows XP.

Hence it implies that it is a great way to defend your computer if you’re still using an outdated version of Windows like Windows XP or Windows Vista.

This image has an empty alt attribute; its file name is button_download.png

10. Emsisoft Emergency Kit

Malware Removal Tool
Emsisoft Emergency Kit

At last, we have the Emsisoft Emergency Kit. This Malware Removal Tool generally concentrates on the core task of managing your PCs free of malware.

It does a great job, and with a clean, simple interface, it seems good too. Its one of the first well-known wicked programs was computer viruses, and the results designed to stop them; therefore, it got the name antivirus as a result.

Emsisoft acknowledges that fact in the goods name, Emsisoft Anti-Malware.

Moreover, it has great scores in malware blocking and wicked URL blocking tests. Not only this, but it also has good scores in lab tests as well.

Furthermore, it also has an effective behavior-based disclosure that can even spot ransomware as well. 

This image has an empty alt attribute; its file name is button_download.png

Conclusion

So, in the above article, we have explained the top 10 best malware removal tool of 2022.

Well, the above list can go on, but it depends on the selection of the right tool and correct procedures.

Thus, some of the tools are free to use so users can efficiently and effortlessly use it and can check whether any virus is entered or not, and you can also quickly determine which is more suitable for you.

The tools mentioned above will surely help you to defend your PC or laptop.

Hence, if you liked this post, then simply do not forget to share this post with your friends, family and on your social network profiles as well.

Adblock test (Why?)


You may be interested in:
>> Is a Chromebook worth replacing a Windows laptop?
>> Find out in detail the outstanding features of Google Pixel 4a
>> Top 7 best earbuds you should not miss

Related Posts:
>> Recognizing 12 Basic Body Shapes To Choose Better Clothes
>>Ranking the 10 most used smart technology devices
>> Top 5+ Best E-readers: Compact & Convenient Pen
Read More
  • Share This:  
  •  Facebook
  •  Twitter
  •  Google+
  •  Stumble
  •  Digg

How to Talk to ChatGPT: An Intro to Prompt Engineering

 December 17, 2022     No comments   

ChatGPT, GPT-3, DALLE, MidJourney, Stable Diffusion…

What do all of these AI models have in common? Other than being way too expensive to create and very complicated to understand unless you watch my articles ;), they are all models regular people like us can use to generate amazing results or even create products through prompting.

Prompting is pretty much the only skill you now require to be a master of these new large and powerful generative models, whether it be to generate cool stories, amazing images, or any cool feature like a text summarizer or automatic video editor tool.

The results of these models are only getting better with time, but it is often hard to get exactly what you are looking for. While this is also only improving, the best way to leverage these large models’ potential is to be a better prompt engineer.

But what is a prompt engineer? Moreover, what is this prompting thing I have been talking about for the past minute or so and how can we learn this skill and get better?! Well, that’s exactly what we are going for in this video…

References

►Learn Prompting: https://learnprompting.org/
►Our Twitter accounts: https://twitter.com/Whats_AI https://twitter.com/SanderSchulhoff https://twitter.com/towards_AI https://twitter.com/learn_prompting
►Discord: https://www.louisbouchard.ai/learn-ai-together/

Video Transcript

0:00

chat GPT gpt3 Dali mid-journey stable

0:04

diffusion what do all these AI models

0:06

have in common other than being way too

0:09

expensive to create and very complicated

0:11

to understand unless you watch my videos

0:13

they are all models Regular People Like

0:16

Us can use to generate amazing results

0:18

or even create products through

0:20

prompting prompting is pretty much the

0:22

only skill you now require to be a

0:25

master of these new large and Powerful

0:27

generative models whether it be to

0:29

generate cool stories amazing images or

0:32

any cool feature like a text summarizer

0:34

or automatic video editor tool the

0:37

results of these models are only getting

0:39

better with time but it's often hard to

0:41

get exactly what you are looking for

0:43

while this is also only improving the

0:45

best way to leverage these large models

0:47

potential is to be a better prompt

0:50

engineer but what is a prompt engineer

0:52

moreover what's this prompting thing I

0:55

have been talking about for the past

0:57

minute and how can we learn this skill

0:59

and get better well that's exactly what

1:02

we are going for in this video

1:04

prompting is how humans can talk to AIS

1:07

it's a way to tell the AI what you want

1:10

and how you want it usually done with

1:12

words for example you might want to

1:14

generate an image but have nothing to

1:16

show it as an example what would you do

1:19

you'd do the same thing as with an

1:21

artist you will hire try to describe

1:23

what you want with the best words

1:25

possible and some sketches if you can

1:27

draw this is the same thing with today's

1:29

most powerful AIS

1:31

as we saw in my previous video about

1:33

word embeddings AIS can understand words

1:36

though they understand them differently

1:39

than we do this is where prompt

1:41

engineering comes into play prompt

1:43

engineering is the task of finding the

1:45

prompt that gets the best results from

1:48

the AI a prompt engineer will translate

1:50

your ID into words that the AI can

1:53

understand it's a translator between

1:55

human language to AI language you can

1:58

see print engineering as the same as an

2:00

expert googler lots of people get hired

2:03

simply because they know how to use

2:05

Google well and get answers to their

2:07

questions especially programmers

2:09

compared to your dad who may struggle to

2:12

find what he wants that's because you

2:14

know what Google's search box is

2:16

expecting and which keywords are good or

2:19

not whereas your dad does not he's

2:21

typing as if he's asking a question to

2:24

another human being which the machine

2:26

cannot understand nearly as well

2:28

let's dive into some examples of how

2:31

learning prompting skills can help you

2:33

out in your AI Journey then we'll dive

2:35

into a very cool prompting course my

2:37

friend sander and I are working on to

2:39

help you improve this communication

2:41

skill and become a real prompt engineer

2:45

text prompting is a way to talk to

2:47

language models the best way to

2:49

understand this is by looking at a

2:51

simple example let's ask gpt3 to solve a

2:54

math problem we can see that it will get

2:56

the wrong answer however we can further

2:59

adapt it to the AI like the simple

3:01

addition of let's think step by step and

3:05

it will succeed image prompting is quite

3:08

similar we can use words to describe an

3:10

image to a text to image model and see

3:13

what it generates we see that as we

3:16

change different descriptors the images

3:18

that the model generates change

3:20

accordingly the code behind prompt

3:22

engineering is to optimize that we

3:25

believe it's important to learn this new

3:27

skill as large language models will only

3:29

become more available and more powerful

3:32

it's obvious that people will get paid

3:34

just to use and master them and we want

3:37

to help you reach that to this end along

3:40

with my friend sender and tours AI we

3:43

are building a course on planting called

3:44

called line prompting where you can

3:47

learn a lot about good printing

3:48

practices and cool techniques or even

3:51

tips from experts specifically oriented

3:54

toward the model you are tackling

3:55

whether it's chat GPT mid-journey or

3:58

anything else check it out to learn more

4:00

about printing and get insights from

4:03

experts in the field this is an open

4:05

source work in progress and we aim to

4:08

continually improve this course and add

4:10

cool new sections over time we'd love it

4:13

if you want to contribute and share your

4:15

knowledge as well with more people

4:17

through this platform join the learn AI

4:20

together community and Discord to learn

4:22

more about this new course and chat with

4:25

us all the links are in the description

4:27

below thank you for watching the video

4:29

and follow me sander and towards the eye

4:32

on Twitter to stay up to date with the

4:34

new sections in this course

L O A D I N G
. . . comments & more!

Adblock test (Why?)


You may be interested in:
>> Is a Chromebook worth replacing a Windows laptop?
>> Find out in detail the outstanding features of Google Pixel 4a
>> Top 7 best earbuds you should not miss

Related Posts:
>> Recognizing 12 Basic Body Shapes To Choose Better Clothes
>>Ranking the 10 most used smart technology devices
>> Top 5+ Best E-readers: Compact & Convenient Pen
Read More
  • Share This:  
  •  Facebook
  •  Twitter
  •  Google+
  •  Stumble
  •  Digg
Newer Posts Older Posts Home

Copyright © Linchakin | Powered by Blogger
Design by Hardeep Asrani | Blogger Theme by NewBloggerThemes.com | Distributed By Gooyaabi Templates